top of page
FlutterCon_logo.png

21 NOVEMBER, 2026

BANGALORE
FlutterCon_icon_turned.png
Anita_Singh_edited.jpg

( SPEAKER )

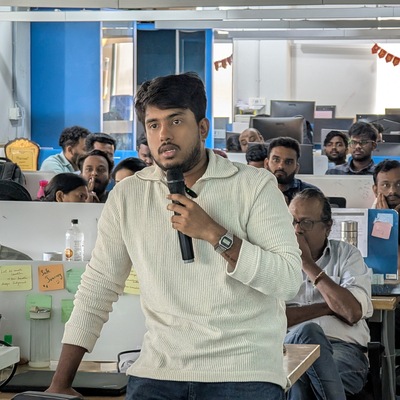
Bornak Paul

Team Lead (Flutter)

Nitara

Bornak Paul is a Team Lead at NITARA (GormalOne LLP), where he leads the development of Flutter applications and backend services used by thousands of users in the dairy-tech ecosystem. With over four years of experience building production-grade mobile and backend systems, he specializes in Flutter, Spring Boot, AWS, and mobile application security.

Passionate about sharing practical engineering lessons, Bornak enjoys exploring scalable architectures, application security, and AI-powered mobile solutions. In this session, he shares real-world insights into defending Flutter applications against Man-in-the-Middle (MITM) attacks using certificate pinning, along with the production challenges and trade-offs every Flutter developer should understand.

Unconference Roundtable

Hardening Flutter Security: Balancing Compliance & Operational Risks

Implementing enterprise-grade security features like certificate pinning, local database encryption, and biometric enclaves is no longer optional for high-stakes production apps. However, these hardcore security measures create a massive operational tension: the tighter you lock down the client application against external attacks, the more brittle it becomes in production. A single out-of-sync encryption key rotation or a misconfigured security policy can instantly lock out entire cohorts of legitimate users and completely stall your release cycle. This roundtable is a tactical discussion for developers navigating the complex world of mobile application security and data protection. We will move away from theoretical encryption math to focus on the broad, real-world realities of keeping apps secure without breaking day-to-day operations. Join us to share your strategies for managing runtime keys, setting up robust fallback systems, and surviving emergency security rotations when things go wrong in production.

Lightning talk

Beyond HTTPS: Preventing MITM Attacks in Flutter with Certificate Pinning

HTTPS is often considered the gold standard for securing mobile applications—but is it enough? In this session, we'll explore how a Flutter application's HTTPS traffic can still be intercepted through a Man-in-the-Middle (MITM) attack using widely available proxy tools. We'll understand why this happens, how certificate pinning prevents it, and what it takes to implement it correctly in Flutter. Using a practical demonstration, we'll walk through intercepting a Flutter app's network traffic, securing it with certificate pinning, and discussing the production challenges that come with it—including certificate rotation, debugging, backup pins, and knowing when certificate pinning may not be the right solution. Whether you're building enterprise, fintech, healthcare, or consumer applications, this session will equip you with practical techniques to strengthen your app's network security while understanding the trade-offs involved.
bottom of page